Skip to content

Enterprise-Grade | MENA & Global

Security.Systems.Software.

We design and operate the deep layers of modern infrastructure — penetration-tested, architected for scale, and engineered with intent. From offensive security to cloud architecture to custom development.

Three pillars

The depth of technology, in three deliberate layers.

Each pillar is its own discipline. Each is engineered by specialists. Together, they form the foundation we build for every client.

01 / 03Pillar one

Security

Advanced threat detection and prevention for digital infrastructure.

Offensive-first security: we find the gaps before attackers do. From penetration tests to compliance management, we harden every layer.

  • Penetration Testing
  • Vulnerability Assessment
  • Security Audits
  • Incident Response
  • Compliance Management
  • Red & Blue Team

02 / 03Pillar two

Systems

Scalable, resilient architecture engineered for the workloads of tomorrow.

We design systems for failure as much as for success — multi-region, fault-tolerant, observable. Built to outlast the next decade.

  • Infrastructure Design
  • Cloud Architecture
  • High Availability
  • Disaster Recovery
  • Performance Tuning
  • Cost Optimization

03 / 03Pillar three

Software

Custom software that earns its place in your stack — and stays maintainable.

Bespoke development from the database to the deploy script. Modern stacks, clean foundations, real test coverage. AI when it actually helps.

  • Custom Development
  • API Integration
  • Data & Analytics
  • AI / ML Solutions
  • DevOps Automation
  • Mobile & Web

Capabilities

A complete spectrum of expertise under one roof.

From the boardroom to the kernel — capabilities tuned for enterprise teams operating across regulated industries.

  • 01 — SEC

    Penetration Testing

    Adversarial assessments of applications, networks, and cloud environments.

  • 02 — SEC

    Vulnerability Mgmt

    Continuous scanning, prioritization, and remediation workflows.

  • 03 — SEC

    Compliance

    ISO 27001, SOC 2, GDPR, PCI-DSS alignment and audit support.

  • 04 — SYS

    Cloud Architecture

    AWS, Azure, GCP — designed for high availability and cost-efficient scale.

  • 05 — SYS

    Disaster Recovery

    RTO/RPO planning, multi-region failover, and continuity drills.

  • 06 — SYS

    Performance Tuning

    Profiling, caching, and infrastructure optimization at scale.

  • 07 — SFT

    Custom Development

    Bespoke applications built on modern stacks with maintainable foundations.

  • 08 — SFT

    API Integration

    Third-party connectors, internal SDKs, and event-driven systems.

  • 09 — SFT

    AI / ML

    Retrieval, fine-tuning, and production deployment of ML pipelines.

Tools

Products we build and run.

Software from the ABYSSS team, from free lookups anyone can use to paid platforms for businesses and MSPs.

Email security

Postward

Complete email security without the risk.

DMARC monitoring, phishing simulation and security awareness training in one platform. Postward never manages your DNS or sits in your mail path: it only receives DMARC reports, so your mail keeps flowing whatever happens to it.

  • Free plan
  • Paid plans
  • Free tools, no account
Open Postward (opens in a new tab)

Articles

Field notes worth reading.

Practical guides from our team, for the people who run and defend real systems.

  • Security Leadership22 min read

    You Will Get Hacked. Your Job Is to Make It Expensive.

    Perfect security does not exist, and AI is cutting the cost of attack. A CISO’s guide to the threat cost ladder, the board conversation and raising the price of compromising you.

  • Incident Response25 min read

    Windows Cyber Triage for Incident Response

    A hands-on triage playbook for compromised Windows hosts: memory capture, live response, persistence hunting, event logs, execution artifacts, KAPE and Velociraptor collection.

  • Incident Response22 min read

    Linux Cyber Triage for Incident Response

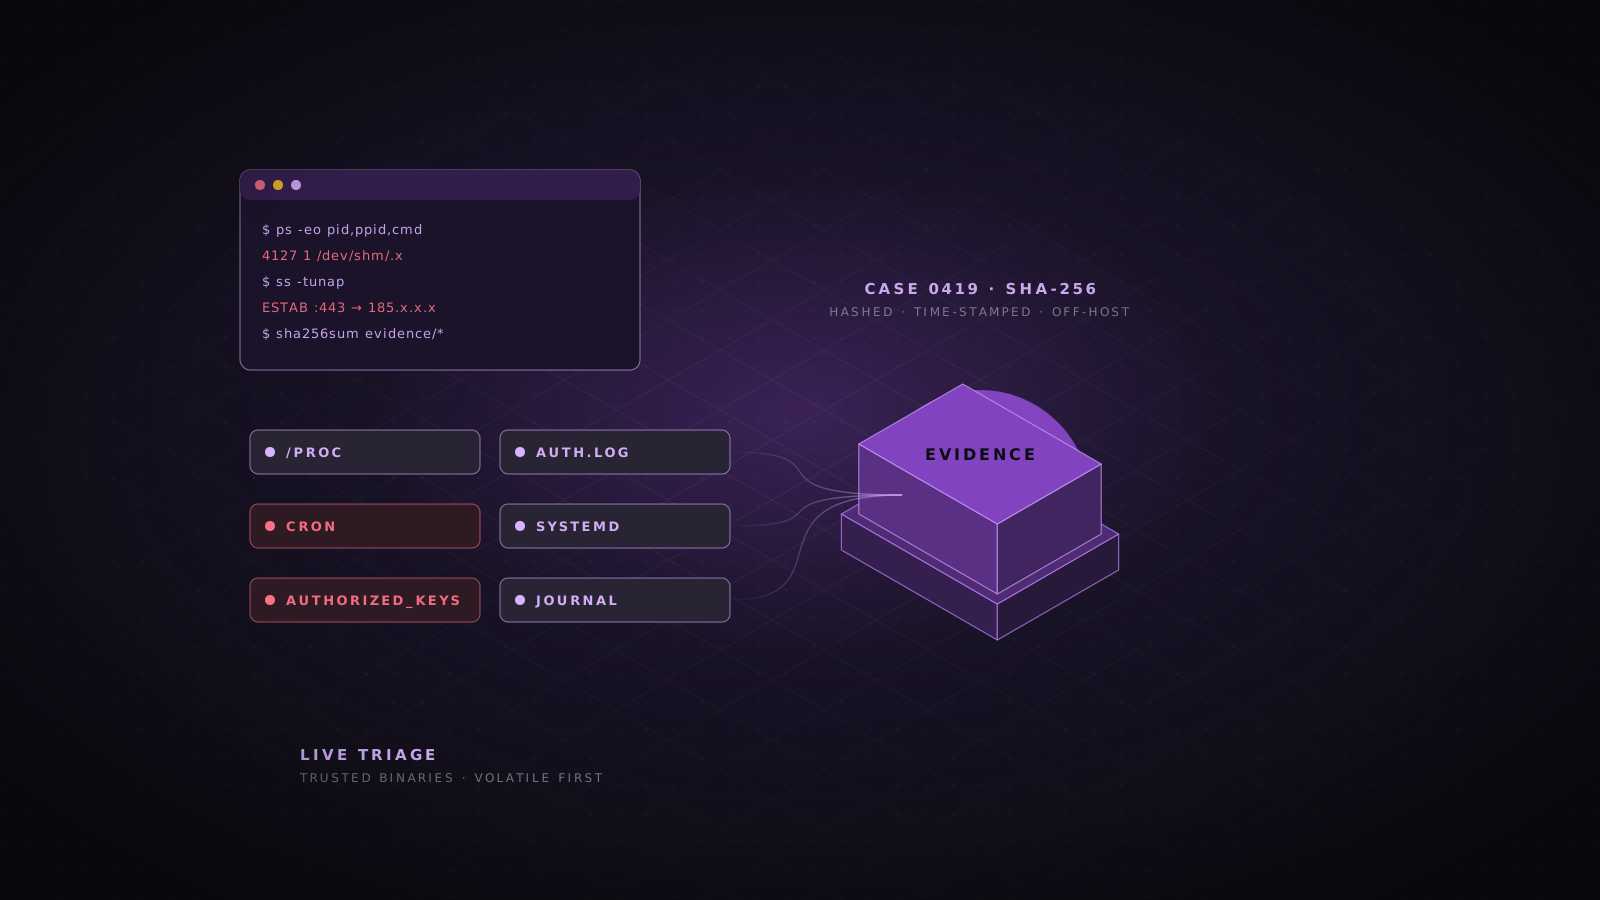
    A hands-on triage playbook for compromised Linux servers and containers: memory capture, /proc analysis, SSH keys, logs, persistence hunting, rootkit checks and UAC collection.

  • Security Operations3 min read

    Getting Real Value from SIEM, SOAR and Security AI

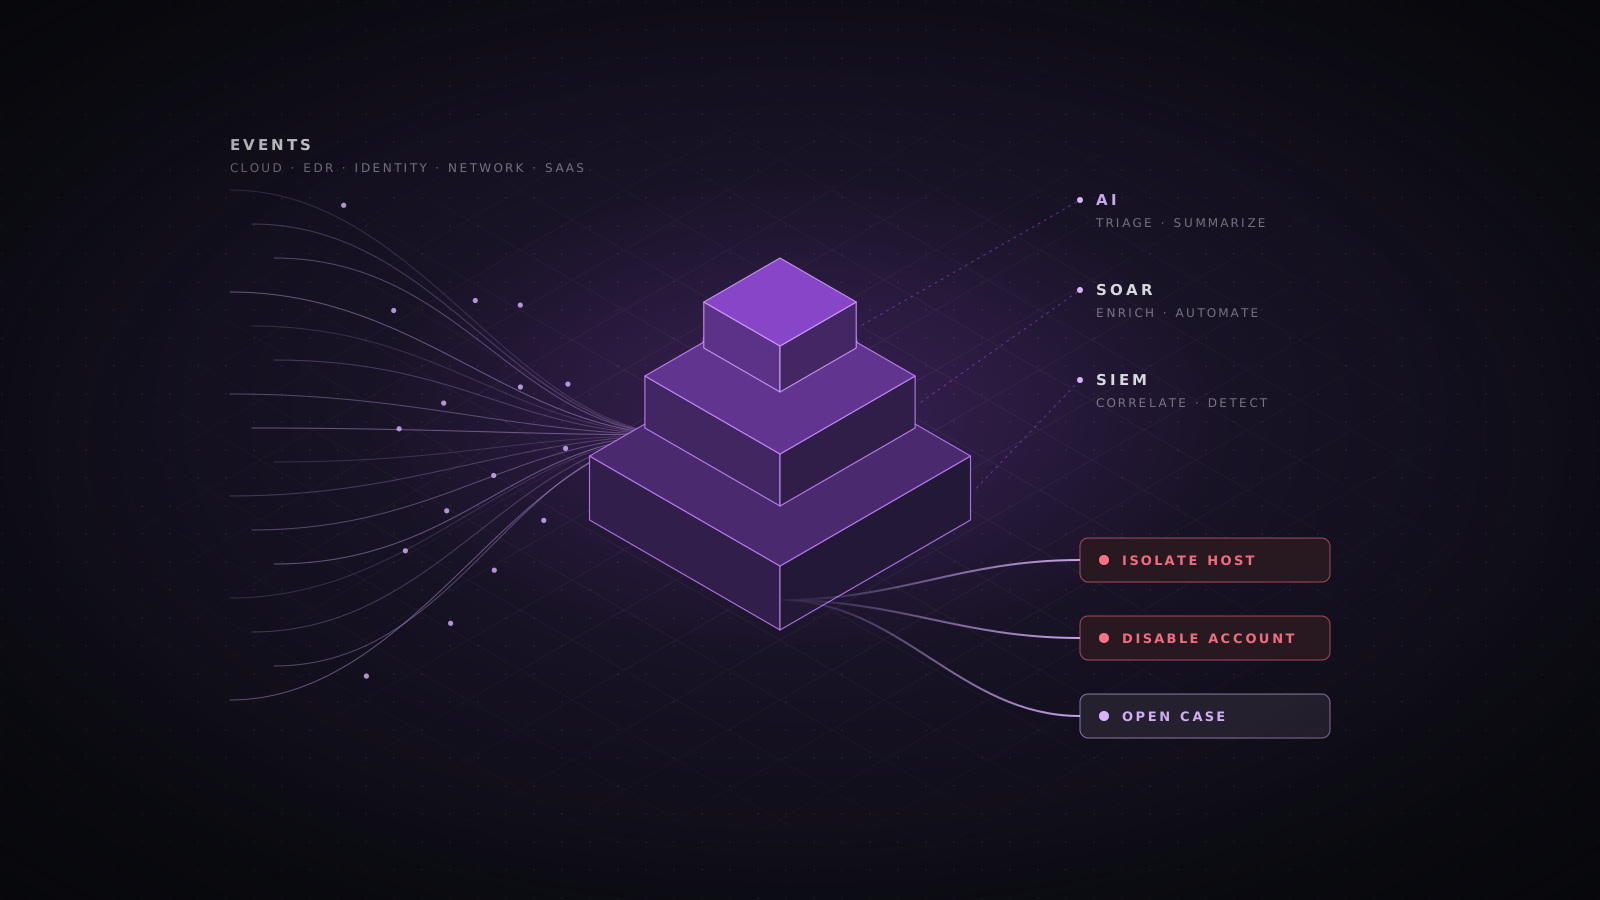
    Why many SIEM deployments disappoint, how to build one that catches real attacks, and how that foundation makes SOAR automation and AI-assisted analysis worth having.

FAQ

Questions, answered.

If your question isn't here, write us directly — most replies go out within one business day.

We layer defenses across the stack — network segmentation, identity and access management, endpoint hardening, application-level controls, and runtime monitoring. Engagements typically start with a threat model so we can prioritize the controls that matter for your business.

We design for horizontal scale from day one — stateless services, queue-decoupled components, autoscaling policies, and load-tested capacity headroom. We benchmark every architecture against realistic traffic profiles before it ships.

Discovery → architecture → iterative build with weekly checkpoints → security review → hardened release. Every project gets infrastructure-as-code, CI/CD, and runbooks at handoff.

Yes — retainer-based engagements with defined SLAs, on-call rotation, and quarterly architecture reviews. We can also embed alongside your internal teams during high-stakes periods.

Almost always. We're stack-agnostic and have deep experience with legacy systems integration, ESBs, custom APIs, and incremental modernization patterns like strangler-fig.

Financial services, healthcare, government, e-commerce, and high-growth technology companies — anywhere security and reliability are non-negotiable.

Get in touch

Let's build the deep layer of your next system.

Tell us about your project. We'll respond within one business day with next steps and an outline of how we'd approach the work.

Based in
Beirut, Lebanon
Serving the Middle East & beyond
Response time
Under 1 business day